Smart industrial site with robots, industrial vehicles and secure private 5G connectivity

Private mobile networks, made operational

Own the network.
Control the operation.

KAOKAB gives enterprises and service providers a controlled operating model for private 5G—from central service visibility to resilient execution at every Edge site.

  • Central visibility
  • Local Edge control
  • Tenant-aware operations
  • Secure support access

One operational scope

Central coordination. Local continuity. One private mobile network.

KAOKAB connects the responsibilities that make private mobile networks dependable, from coordinated operations to resilient execution at each site.

  1. NOC — Central coordination

    Role-aware visibility and managed support.

  2. Edge — Local execution

    Site-local lifecycle and service continuity.

  3. Private 5G — Private mobile network

    Core, radio access, SIMs and devices.

One company. Two operational products.

Central coordination and local execution, designed as one KAOKAB system.

KAOKAB NOC and KAOKAB Edge share one operating model and one visual identity. Each product keeps a clearly defined responsibility.

KAOKAB NOC

Central network operations

Coordinate providers, customers, inventory, licensing, events and authorized support from the central operational control plane.

Explore the platform

The NOC portal is restricted to authorized users. Public registration is not available.

Access NOC Platform
KAOKAB EDGE

Local private-network operations

Run and validate the site-local core, RAN integration, data path, health controls and recovery lifecycle close to the network.

Explore KAOKAB Edge

NOC to Edge

One operating model from central visibility to local execution.

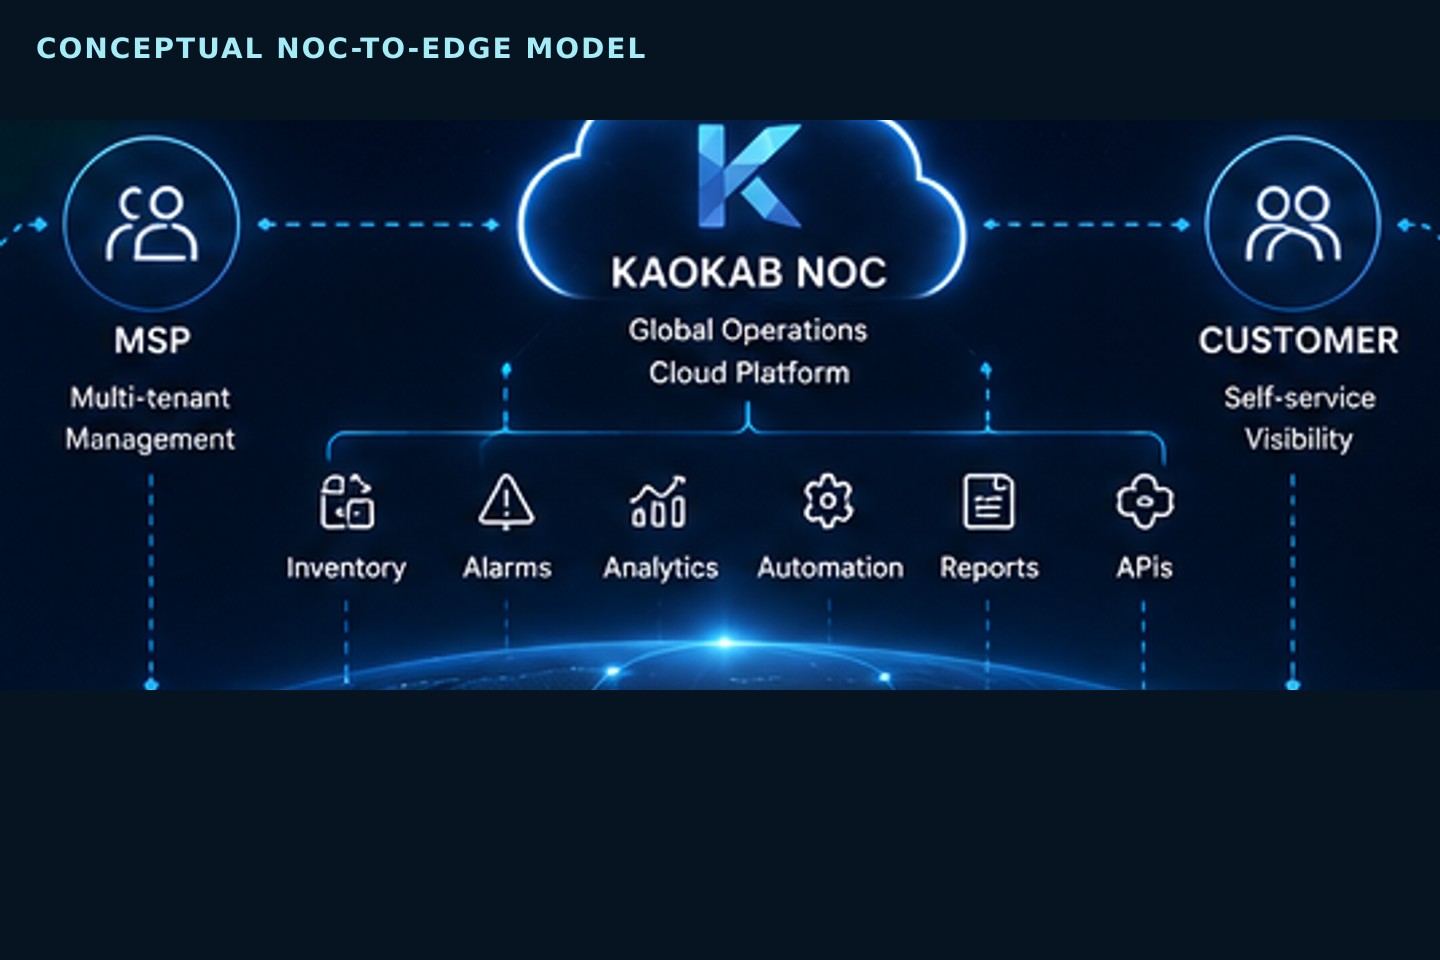
The relationship shown here is a conceptual marketing view of the documented KAOKAB operating model: role-aware NOC operations connected with Edge responsibilities.

  1. Central

    Providers, customers, inventory and licensing are coordinated from the NOC.

  2. Managed path

    Authenticated management connectivity carries visibility and support actions.

  3. Local

    Edge sites run the site-local core, radio integration and recovery lifecycle.

Conceptual diagram showing KAOKAB NOC connected to MSP, customer and operational platform areas
KAOKAB NOC-to-Edge operating modelConceptual marketing artwork; not production platform evidence.

Capabilities

The operational tools behind a dependable service.

A focused set of capabilities helps teams manage the full service context without turning the public website into a technical console.

  • Guided deployment

    Use controlled workflows to prepare, validate and activate Edge configurations with clear operational checkpoints.

  • Multi-tenant operations

    Organize platform, service-provider and customer responsibilities through separated views and role-based access.

  • Edge lifecycle

    Track Edge identity, assignment, connectivity and operational state from onboarding through ongoing support.

  • SIM and device inventory

    Maintain the service relationship between SIMs, access points, Edge systems, customers and providers.

  • Health and events

    Bring platform and service events into context so teams can identify what needs attention and where.

  • Secure remote support

    Provide controlled support paths to distributed Edge environments while keeping operational access explicit.

Architecture

Central coordination. Local execution. Clear boundaries.

The KAOKAB NOC provides the operational control plane for service management. KAOKAB Edge runs the local private-network environment and reports the status needed for lifecycle and support workflows. This separation keeps responsibilities understandable and allows each deployment to preserve its required local services.

Central coordination. Local execution. Clear boundaries.
KAOKAB NOCTenants, inventory, licensing, events and operational workflows
KAOKAB EdgeLocal runtime, network functions and controlled support endpoint
Private mobile networkRAN, SIM-enabled devices and site services

Built around responsibility

The right operational context for every role.

  • Managed service providers

    Operate assigned customers and Edge estates from a separated service-provider workspace.

  • Enterprise customers

    See the networks, inventory and service information relevant to the customer environment.

  • Edge operations

    Run local private-network functions and expose the operational state required for remote support.

Security

Operational security is part of the architecture.

KAOKAB is designed around separated responsibilities, authenticated access and controlled connectivity between central operations and distributed Edge environments.

Explore KAOKAB security
  1. Tenant separation

    Keep provider and customer operational views within their assigned scope.

  2. Role-based access

    Match platform actions and information to authenticated user responsibilities.

  3. Controlled Edge connectivity

    Use defined management paths for remote visibility and support.

  4. Operational resilience

    Support backups, recovery procedures and lifecycle validation as part of platform operations.

Built for accountable operations

A private network becomes valuable when teams can operate it with clarity.

KAOKAB brings the service context around radio, core, Edge, subscribers and support into one controlled operating model. The result is a clearer path from technical deployment to an owned, supportable service.

  1. 01

    Responsibility first

    Define who owns the site, service, platform and support decisions before activation.

  2. 02

    Evidence before acceptance

    Use explicit validation checkpoints for configuration, reachability and runtime health.

  3. 03

    Local continuity

    Keep site-critical execution close to the private network and its applications.

  4. 04

    Controlled support

    Separate public presentation, authenticated operations and protected Edge access.

From requirement to operated service

A deliberate route to production—not a technology drop-off.

Every engagement begins with the operational requirement and advances only when the preceding evidence is accepted.

  1. 01

    Discover

    Map sites, devices, applications, mobility, coverage and service ownership.

  2. 02

    Design

    Define the radio, core, Edge, integration and operating boundaries.

  3. 03

    Prove

    Validate the highest-value use case through a focused proof of concept.

  4. 04

    Deploy

    Activate the approved design using controlled installation and health checks.

  5. 05

    Operate

    Maintain lifecycle, inventory, events and support through the appropriate tenant view.

A practical starting point

Where a KAOKAB conversation creates value.

You are evaluating private 5G

Clarify where private mobile adds value alongside existing LAN and Wi-Fi services.

You operate multiple sites

Create a repeatable service model without erasing local technical requirements.

You deliver managed services

Separate provider, customer and site responsibilities inside one operational portfolio.

Evaluation questions

What decision-makers usually ask first.

Does KAOKAB replace radio or mobile-core specialists?

No. KAOKAB provides the operational model that connects specialist radio, core, Edge and enterprise responsibilities. Solution boundaries are agreed for each deployment.

Can private 5G work alongside Wi-Fi?

Yes. Private 5G is positioned where managed mobility, SIM identity, coverage or local service control adds value; Wi-Fi remains essential for many enterprise workloads.

Can services continue if central connectivity is interrupted?

The architecture is designed so site-local functions can remain at the Edge. The exact continuity behavior depends on the approved local design and application dependencies.

How do we start without committing to a full rollout?

Begin with a bounded discovery and proof of concept focused on representative devices, coverage zones, applications and acceptance criteria.

Start the conversation

Ready to make private 5G operational?

Tell us about your environment, service model or proof-of-concept goals. We will explore where KAOKAB can support your private-network operations.